Trail MapTechnology Risk Management
The Photo-Op Fallacy: Why MVP Thinking Fails in Risk Management
There Are Three Letters I’ve Come to Dread: M-V-P
Over the years, I’ve worked with countless organizations striving to manage risk or respond to regulatory findings-whether through proactive improvement or under the pressure of a consent order, MRA, MRI, or enforcement action. And there are three letters that can change the entire tone of those conversations: M-V-P.
The term Minimum Viable Product (MVP) has earned a hallowed place in business vocabulary since Eric Ries introduced it in The Lean Startup (2011), expanding on Steve Blank’s customer development model. Its intent was simple yet powerful: build the smallest functional version of an idea to learn what stakeholders actually value before investing heavily in the wrong direction.
Used correctly, it’s about experimentation, feedback, and refinement-an iterative path toward excellence. But when organizations import that mindset into risk management and regulatory remediation, something critical gets lost in translation.
When MVP Becomes “Minimum Viable Proof”
Somewhere along the way, “Minimum Viable Product” in risk management and regulatory compliance has became synonymous with “Minimum Viable Proof” - the smallest defensible action an organization can take to say “we’ve done something”. This view drive optics and avoidance instead of discovery and improvement in how risks are managed or compliance obligations are addressed.
I’ve seen it time and again: remediation plans framed around the question, What’s the minimum we can deliver to satisfy the regulators or auditors? This includes:
-
Control enhancements that look impressive on paper but fade the moment oversight eases.
-
Teams that treat remediation as a project to be closed, not a process to be strengthened.
The result? A culture that prizes compliance theater over true control effectiveness. A cycle of short-term fixes that fail to evolve as risks, technologies, and expectations change.
The Photo-Op Fallacy
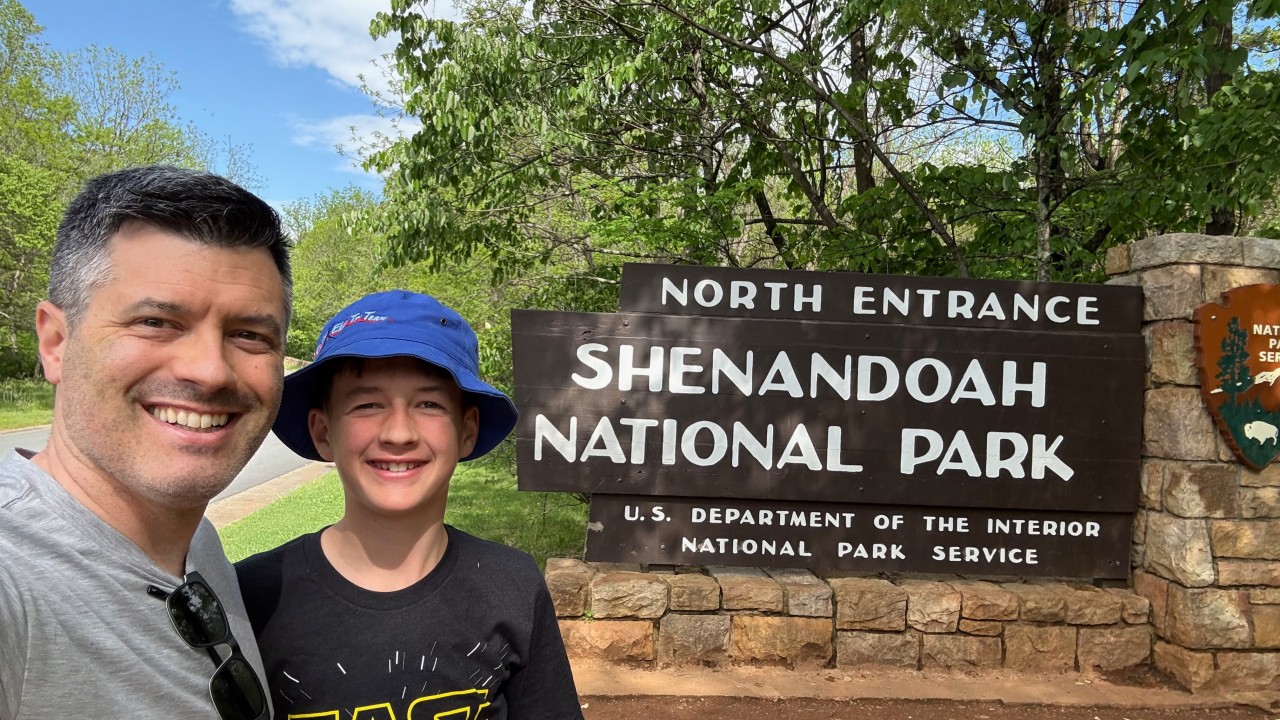
It reminds me of something I’ve been guilty of once or twice myself-working toward the goal of visiting every national park but only stopping long enough to take a picture with the entrance sign. You can claim you’ve been there. You can check the box. But you’ve missed the experience-the trails, the vistas, the ecosystems that make each park unique.
That’s how many organizations treat MVP in risk management. They stop at the sign, capture evidence, and move on. The documentation looks good. The dashboard turns green. But they never explore the full terrain of the risk landscape or learn from the journey.
They treat the MVP as a photo-op not a foundation for progress.
Why It Happens
The irony is that both organizations and regulators contribute to this dynamic. Tight deadlines for regulatory responses, coupled with internal pressure to demonstrate quick wins, create an environment where speed trumps substance.
-
Teams fear that revisiting a remediation approach could signal indecision or noncompliance.
-
Leaders worry that asking to pivot mid-course might be perceived as backtracking rather than learning.
-
REgulators, bound by procedural timelines, don’t signal that iteration is not only acceptable but expected.
The result is a fixed mindset masquerading as agility.
But here’s the thing: true agility isn’t about finishing faster. It’s about learning faster.
Regulators themselves have acknowledged this principle, even if indirectly. Frameworks like the OCC’s guidance on corrective action planning encourage management to adjust plans as conditions evolve. The OCC’s Heightened Standards emphasize ongoing improvement of risk governance. And global principles such as Basel’s BCBS 239 call for adaptability and feedback loops in risk processes.
In other words, iteration isn’t a loophole-it’s a best practice.
The Cultural Cost of Minimum Thinking
When the concept of “minimum” takes center stage, it sends a powerful signal: that management’s risk tolerance is high and thoroughness is negotiable. Over time, that mindset corrodes an organization’s risk culture.
Employees learn that meeting deadlines matters more than achieving durable outcomes that mitigate risk. Controls are designed to satisfy inspection, not withstand stress. Technology solutions are built for visibility, not resilience. And once the oversight light fades, so does commitment to improvement.
I’ve seen organizations struggle to pivot away from tools or processes that no longer make sense because they fear contradicting a prior regulatory submission. Instead of saying, we learned something new and better, they cling to an outdate plan out of fear of being seen as inconsistent.
That’s not risk management. That’s risk stagnation.
Redefining the V in MVP
To reclaim the intent behind MVP, organizations must shift their focus from Minimum to Viable. In a risk and compliance context, viable doesn’t mean barely sufficient - it means value-driven, verifiable, and iterative.
A “viable” solution is one that can be sustained, measured, and improved. It’s a living process that adapts to changes in technology, regulation, and operating conditions. It’s the beginning of a journey, not the end.
Instead of asking, What’s the least we can do?, organizations should be asking, What will make this control truly effective and enduring?
And for regulators, it means recognizing that flexibility does not equal leniency.Encouraging iteration and feedback builds stronger, safer institutions in the long run.
The Path Forward: From Proof to Progress
To move beyond the photo-op fallacy, both management and regulators must be willing to change their perspective:
For management:
-
Stop measuring success by closure dates or submission milestones.
-
Foster a culture where iteration is rewarded and learning is valued.
-
Build remediation plans that include feedback loops and checkpoints for recalibration.
-
Treat regulatory engagement as a partnership for safety and soundness, not a transaction to end scrutiny.
For regulators:
-
Signal openness to adaptation when organizations demonstrate thoughtful reasoning and data-backed improvements.
-
Encourage transparency around lessons learned rather than perfection on first submission.
-
Recognize that the most compliant organization isn’t the one that finishes fastest - it’s the one that continues improving.
Risk management and compliance are not destinations. They’re journeys through complex terrain that demand curiosity, persistence, and humility. If we want to reach the summit safely, we need to do more than snap a picture at the trailhead.
Call to Action
-
Reevaluate your organization’s use of “MVP” in the context of risk and remediation efforts. Does it mean learning and iteration or the bare minimum?
-
Encourage dialogue between compliance teams, executives, and regulators about when and how to adapt remediation plans.
-
Shift the narrative from completion to capability - define success as the ability to sustain and evolve controls, not just close them.
-
Celebrate iteration. Build internal mechanisms that reward improvement and transparency over optics.
-
Ask better questions: Are we truly exploring the landscape, or just taking a photo at the sign?
How does your organization balance regulatory expectations with the need to learn and adapt? Have you ever seen an MVP approach succeed in building lasting risk management improvements? Let me know your thoughts and experiences in the comments!